6 Signs a CMMC Consultant Is Built for Readiness
Hiring a CMMC consultant is an important step toward meeting your CMMC requirements. But hiring a...
One of the most common questions defense contractors ask is:
"What CMMC compliance requirements apply to my organization?"
It's a fair question. Between different contract requirements, multiple assessment paths, and ongoing changes to the Cybersecurity Maturity Model Certification (CMMC) program, it can be difficult to know where to start.
The short answer: CMMC requirements depend on the type of information you handle under each contract. Contracts involving Federal Contract Information (FCI) require CMMC Level 1 self-affirmation. Contracts involving Controlled Unclassified Information (CUI) require CMMC Level 2, self-assessment or a third-party certification. The level specified in the contract is what ultimately determines your compliance level.
Determining which requirements apply is usually more straightforward than many organizations think.
What information is being handled
Which contracts require that information to be protected
Where that information is being processed, stored, or transmitted
Before investing time and resources into remediation efforts or assessment preparation, it's important to understand what CMMC compliance requirements apply in the first place.
A simple way to think about CMMC applicability is:
Information → Contract → Systems → Assessment Requirements
Many organizations jump straight to questions about assessments. In reality, those answers usually become much clearer after identifying the information, contracts, and systems involved.
Do we handle Federal Contract Information (FCI)?
Do we handle Controlled Unclassified Information (CUI)?
Which contracts involve that information, and does any of it come to us through a prime contractor?
Which systems process, store, or transmit FCI/CUI?
Look for the CMMC level identified in the solicitation, including any applicable DFARS provisions and clauses that specify cybersecurity requirements.
What assessment requirements apply?
The answers help establish the boundaries of an organization's CMMC obligations and prevent unnecessary assumptions about what may or may not be required.
Most importantly, organizations shouldn't assume they have one universal CMMC requirement simply because they operate in the Defense Industrial Base (DIB). Requirements often need to be evaluated on a contract-by-contract basis.
This applies to subcontractors too.
Prime contractors are expected to flow CMMC requirements down to their suppliers, and the level that applies to a subcontractor depends on the information shared under that subcontract. It is not necessarily the level the prime holds. Most large primes have sent open letters to their suppliers requiring a CMMC level regardless of what the DoW has on pause.
When a contract includes CMMC Level 1 requirements, organizations that handle Federal Contract Information (FCI) need to meet them.
FCI is information not intended for public release that is provided by or generated for the government under a contract to develop or deliver a product or service.
It does not include information the government makes public or simple transactional information, such as what’s needed to process payments.
CMMC Level 1 focuses on basic safeguards for protecting FCI and includes the 15 security requirements outlined in DFARS clause 252.204-7021.
Those safeguarding requirements already apply to contracts that include the FAR clause, whether or not CMMC is specified.
This is also where many contractors get confused.
Determining whether you have FCI is important, but it isn't the whole story.
Organizations also need to understand:
Which contract the information supports
Where the information is processed, stored, or transmitted
Which systems are involved
Who has access to the information
Identifying FCI is only one part of determining CMMC scope.
Without that context, organizations can end up including far more of their environment than necessary or overlooking systems that should be considered.
A good place to start is by tracing where the information travels throughout the organization. Any computer, cloud service, email inbox, or individual that stores, processes, or transmits the data may fall within scope.
From there, organizations can look for opportunities to eliminate unnecessary data flows or limit where the information resides. Keeping FCI contained to specific systems and processes can help reduce scope, making compliance efforts more manageable and focused.
Level 1 serves as a foundation for broader defense contractor compliance efforts.
Handling Controlled Unclassified Information (CUI) brings CMMC Level 2 requirements into the conversation.
CUI is unclassified information created, possessed, or owned by the U.S. government that requires safeguarding or dissemination controls under applicable laws, regulations, or government-wide policies. While it is not classified information, it is still considered sensitive and requires specific protections.
Level 2 is built around the 110 security requirements in NIST SP 800-171 Revision 2 and serves as the primary mechanism for protecting CUI. Contracts that include DFARS 252.204-7012 already require contractors handling CUI to implement NIST SP 800-171, independent of CMMC verification.
A common mistake is assuming that:
"We handle CUI."
automatically means:
"We need a C3PAO assessment."
Not necessarily.
The presence of CUI is a major factor, but the contract ultimately determines what type of level 2 assessment is required and how compliance must be demonstrated.
That's why organizations should avoid assuming every contractor handling CUI follows the exact same path.
Once the type of information is clear, the next step is understanding what each level asks organizations to do.
Organizations required to meet CMMC Level 1 implement basic safeguarding such as:
Limiting access to authorized users
Verifying the identity of users and devices before granting access
Protecting information during transmission
Restricting physical access to systems
Controlling who can view or use sensitive information
For many contractors, Level 1 establishes a baseline level of cybersecurity for protecting contract-related information.
Organizations that handle CUI generally face a much broader set of cybersecurity requirements.
The 110 requirements in NIST SP 800-171 are organized into 14 families, including:
Access control
Multi-factor authentication
Audit logging
Incident response
Configuration management
Vulnerability management
Security awareness training
Media protection
Risk assessments
System and communications protection
This is often the point where contractors realize CMMC is about much more than passing an assessment. The requirements are intended to strengthen defense industry cybersecurity and improve the protection of sensitive government information throughout the supply chain.
While requirements should always be verified against the contract, most defense contractors fit into one of the following categories:
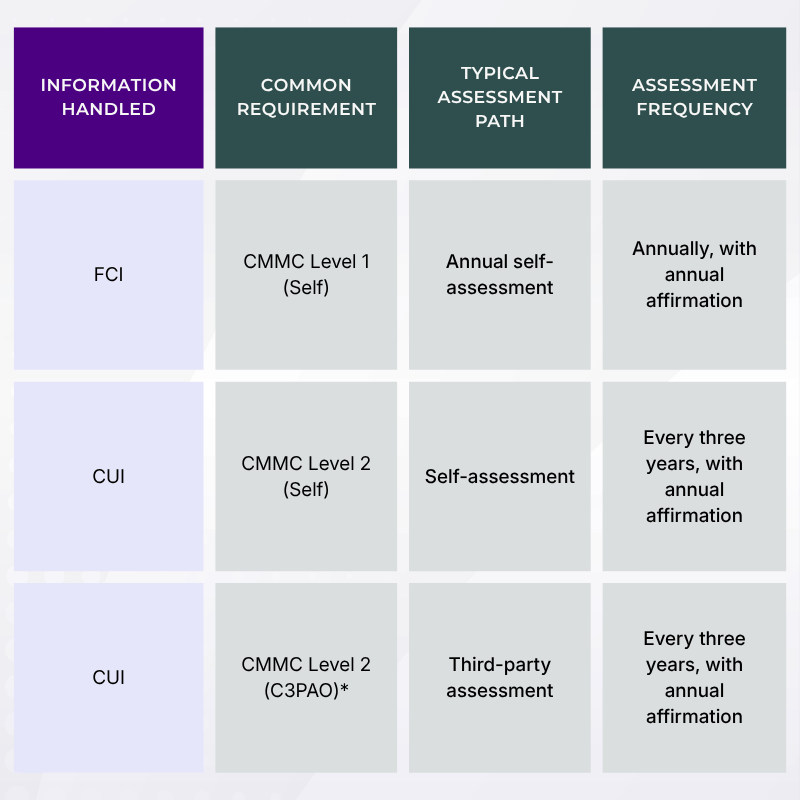
Self-assessment results are submitted in the Supplier Performance Risk System (SPRS), and a senior company official must affirm compliance, so accuracy matters as much as completion.
This isn't a substitute for reviewing the contract, but it provides a useful starting point for understanding where an organization may fit within the CMMC framework.
No.
One of the biggest misconceptions surrounding CMMC is that handling CUI automatically requires a third-party assessment from a Certified Third-Party Assessment Organization (C3PAO).
Under the current CMMC framework, Level 2 can involve either a self-assessment or a C3PAO assessment, depending on what the contract requires.
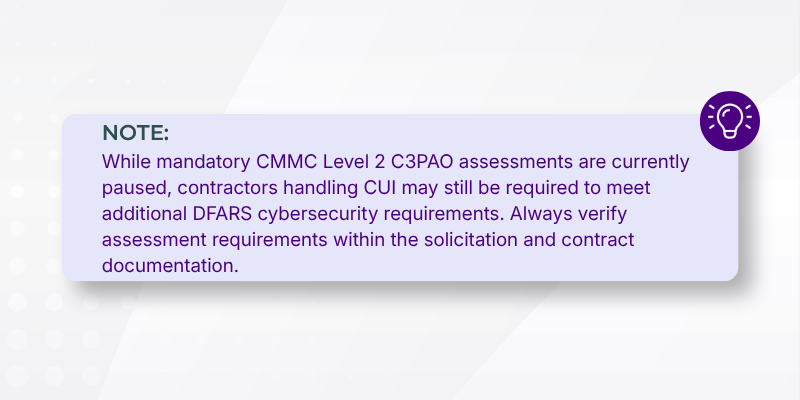
It's also important to separate assessment requirements from recent changes to the Department of War’s pause in the CMMC Phase 2 rollout.
Following that announcement, some contractors interpreted the pause as a sign that CMMC was going away, or that preparation efforts could stop altogether.
That's not the case.
While the pause changed implementation timelines, it didn't remove existing obligations to protect covered information under FAR 52.204-21 and DFARS 252.204-7012. Level 1 and Level 2 self-assessment requirements also remained in place. It also didn't eliminate the need for contractors to understand where they stand against future CMMC requirements.
In many ways, the pause creates an opportunity for more intentional CMMC preparation. Rather than rushing toward a deadline, organizations have additional time to evaluate their environment, address gaps, strengthen documentation, and build a more strategic readiness plan.
Instead of asking:
"Do we need a C3PAO assessment right now?"
Ask:
"What does our contract require, and what do we need to be prepared for?"
Instead of assuming a specific assessment path, start by answering a few key questions:
What CMMC level is specified?
Is the requirement Level 1 Self, Level 2 Self, or Level 2 C3PAO?
Which systems support the contract?
What evidence or documentation will need to be demonstrated?
Those answers provide a much clearer picture of what obligations actually apply.
Determining which CMMC requirements apply is only the first step.
Once an organization identifies the information, contracts, systems, and assessment requirements involved, the focus shifts from applicability to readiness.
At that point, organizations can begin:
Confirming what is in scope
Evaluating current security practices
Identifying compliance gaps
Prioritizing remediation activities
Reviewing required documentation and evidence
Building a long-term compliance strategy
Organizations that establish scope early are often in a much stronger position during readiness efforts because they have a clearer understanding of what requirements apply and what they'll eventually need to demonstrate.
For a more detailed look at the preparation process, see How to Prepare for CMMC in 2026: A Defense Contractor's Complete Guide.
Whether you're trying to determine which CMMC level applies, preparing for an upcoming assessment, or building a long-term compliance strategy, having a clear understanding of your requirements is the first step.
For organizations that self-assess, CMMC Progressing Pathways provides recurring review of documentation and security practices by a Cyber AB-certified expert, helping you find gaps and prepare for CMMC requirements.